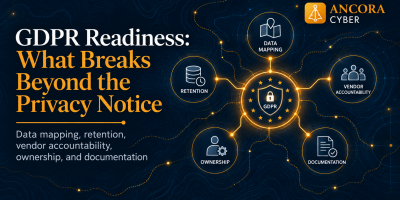
A polished privacy notice can describe a privacy program that does not actually exist.
The real test of GDPR readiness happens behind the notice.
Can your organization identify where personal data enters the business, where it moves, who can access it, which vendors receive it, how long it is retained, and what happens when it should be deleted?
Can the people responsible for those processes explain them?
Can the organization produce evidence showing that those processes actually operate as described?
That is where GDPR readiness becomes an operational governance issue rather than simply a legal or policy exercise.
The GDPR’s accountability model requires organizations not only to comply with applicable data protection requirements, but also to be able to demonstrate that compliance. Records of processing activities, data protection by design, retention practices, processor oversight, and documented responsibilities all contribute to that operational picture.
A privacy notice matters.
But it is only the visible layer.
A useful way to evaluate GDPR readiness is to trace important privacy statements through four layers:
Claim: What does the organization say happens?
Process: What actually happens in day-to-day operations?
Owner: Who is responsible for making sure it happens?
Evidence: What can the organization produce to demonstrate that it happened?
Consider a few common examples.
Claim: Personal data is retained only as long as necessary.
Operational question: Who determines how long each category of data should be retained, and how is deletion triggered?
Evidence may include: retention schedules, documented procedures, system configurations, review records, or deletion records.
Claim: Personal data may be shared with service providers.
Operational question: Which vendors receive personal data, what information do they receive, and why?
Evidence may include: vendor inventories, processing records, contracts, data processing agreements, and documented review processes.
Claim: Individuals may request access, correction, or deletion of their information.
Operational question: Can the organization locate relevant information across the systems where it actually exists?
Evidence may include: documented request procedures, assigned responsibilities, response records, and records showing how requests were completed.
A privacy statement becomes much more defensible when the organization can connect the statement to a real process, a responsible owner, and supporting evidence.
You cannot govern data you cannot locate.
Strong GDPR operations begin with understanding how personal data moves through the organization.
That includes:
This does not necessarily require an enormous technical diagram.
What matters is whether the organization can build and maintain a usable picture of its processing environment.
Records of processing activities can provide an important overview of processing operations, including purposes, categories of personal data, recipients, transfers, storage periods, and security measures.
That information becomes significantly more valuable when it reflects real operations rather than an inventory that was completed once and forgotten.
A practical data map can expose issues that a privacy notice never will.
A SaaS integration may receive customer information that nobody remembered to document.
A legacy system may still contain personal data from a discontinued business process.
A department may have created its own workflow outside the systems included in the original privacy review.
An exported spreadsheet may contain personal information long after the primary system record was removed.
The map is where assumptions begin turning into evidence.
Most organizations understand the idea of data retention.
Operationalizing it is harder.
The GDPR’s storage limitation principle generally requires personal data to be kept only as long as necessary for the purpose for which it is processed, subject to applicable requirements that may justify continued retention.
Writing a retention policy is usually not the hardest part.
Making sure retention actually happens across systems is.
A policy may say that a particular category of information is deleted after a defined period.
But the operational questions continue:
Those questions expose the difference between having a retention schedule and operating one.
The retention policy contains a clear deletion period, but nobody can explain which system performs the deletion, who confirms it occurred, or whether the same rule applies across every location where the information exists.
That is not simply a documentation problem.
It may indicate unclear ownership, incomplete data mapping, or a process that has never been fully operationalized.
Modern organizations depend on cloud platforms, payroll providers, CRM systems, analytics tools, support applications, marketing platforms, and many other vendors that may process personal data.
Privacy operations therefore extend beyond the organization itself.
GDPR responsibilities involving processors can include documented controller-processor relationships, appropriate contractual requirements, security expectations, management of subprocessors, assistance with individual rights, and requirements for handling personal data when services end.
Signing a data processing agreement is important.
It is not the end of vendor governance.
The operational questions continue:
Vendor inventories, contracts, processing records, data maps, retention practices, and internal ownership should connect.
If each exists independently, gaps become much easier to miss.
Procurement has the contract.
Security has the vendor questionnaire.
Operations owns the application.
Privacy has a processing inventory.
But nobody can confidently explain whether all four describe the same relationship.
That is the kind of gap operational readiness should identify before external scrutiny does.
Privacy touches too many parts of a modern organization to live entirely within one department.
Legal may interpret obligations.
Security may protect systems.
IT may manage platforms and access.
Human resources may process employee information.
Marketing may manage customer and prospect data.
Procurement may manage vendor relationships.
Business units may determine why particular information is collected in the first place.
That makes ownership critical.
Someone needs to know:
Operationally, responsibilities cannot remain implied.
Consider a basic individual rights request.
Knowing that an individual has a right is only the beginning.
The organization may need to locate relevant information, coordinate across systems and departments, determine what action is appropriate, communicate with the individual, and document the response.
That becomes much harder when responsibilities are unclear.
Clear ownership makes repeatable privacy operations possible.
One of the most common weaknesses in compliance programs is not a complete absence of documentation.
It is documentation that describes a process that no longer exists.
Businesses change quickly.
A new SaaS application is introduced.
A vendor changes.
A department starts collecting additional information.
A product expands into another market.
A manual process becomes automated.
Responsibility moves from one employee to another.
The documentation often changes more slowly.
That creates drift between what the organization says it does and what it actually does.
Strong GDPR readiness requires periodically reconnecting those two things.
Policies, records of processing activities, retention schedules, vendor inventories, contracts, procedures, security documentation, and public privacy statements should describe the same operating environment.
The goal is not to create more paperwork.
The goal is to create documentation that helps the organization understand its own environment, establish accountability, respond consistently, and demonstrate how privacy requirements are being addressed.
Documentation should reflect reality before scrutiny begins.
Consider a SaaS company that tells customers account data is deleted when the relationship ends.
The primary application follows that process.
The CRM does not.
Historical support tickets remain in a separate platform.
Marketing has exported contact lists into spreadsheets.
A former analytics integration still contains historical records.
Nobody intentionally ignored the privacy policy.
The problem is that the organization never mapped the full deletion process across every system and owner involved.
Changing one sentence in the privacy notice would not solve that problem.
The organization needs to understand the data flow, define ownership, align retention processes, and establish evidence that those processes actually operate.
That is the difference between privacy documentation and operational privacy governance.
A useful GDPR readiness review does not need to begin with hundreds of questions.
Start with five.
If the answer depends on one employee’s memory or an outdated spreadsheet, the data map may need attention.
A retention period without an operating process behind it may not tell the full story.
A signed agreement is important, but so is understanding the actual processing relationship.
If everyone is involved but nobody clearly owns the process, accountability can break down quickly.
If the written program describes last year’s environment, the organization may be relying on documentation that no longer reflects reality.
If these questions are difficult to answer with both an owner and supporting evidence, rewriting the privacy notice is probably not the first problem to solve.
The operational map needs attention.
Privacy readiness becomes much easier to understand when organizations stop treating GDPR as a collection of documents that need to be completed and start treating privacy as an operating discipline.
The privacy notice matters.
Policies matter.
Contracts matter.
Records of processing matter.
But those documents are strongest when they sit on top of processes that can be explained, owned, operated, and demonstrated.
Start with the map.
Understand the data.
Define ownership.
Establish retention discipline.
Know your vendors.
Connect public statements to actual processes.
Align documentation with real practices.
Then maintain that picture as the organization changes.
That is how privacy language becomes defensible privacy operations.
If your organization handles EU personal data and you are unsure whether your privacy documentation reflects how personal data is actually collected, used, shared, retained, and deleted, Ancora Cyber can help clarify the current state.
Ancora works with organizations to map requirements and operations, clarify ownership, identify meaningful gaps, align documentation with reality, and prepare evidence that supports the organization’s privacy and compliance claims.
Book a Mapping Call
Ancora Cyber provides compliance enablement and operational governance support. We do not provide legal advice or act as a regulatory authority.