Student Data Access Control Mistakes That Create FERPA Risk
Most education organizations don’t intentionally create unnecessary access to student information.
Access grows over time.
A teacher changes roles but keeps old permissions. A department adopts a new EdTech platform. A third-party vendor receives broader access during implementation. Temporary administrative permissions are never removed. Shared folders accumulate new users year after year.
CIS Controls Risk Assessment Giveaway at the Arizona Technology Summit
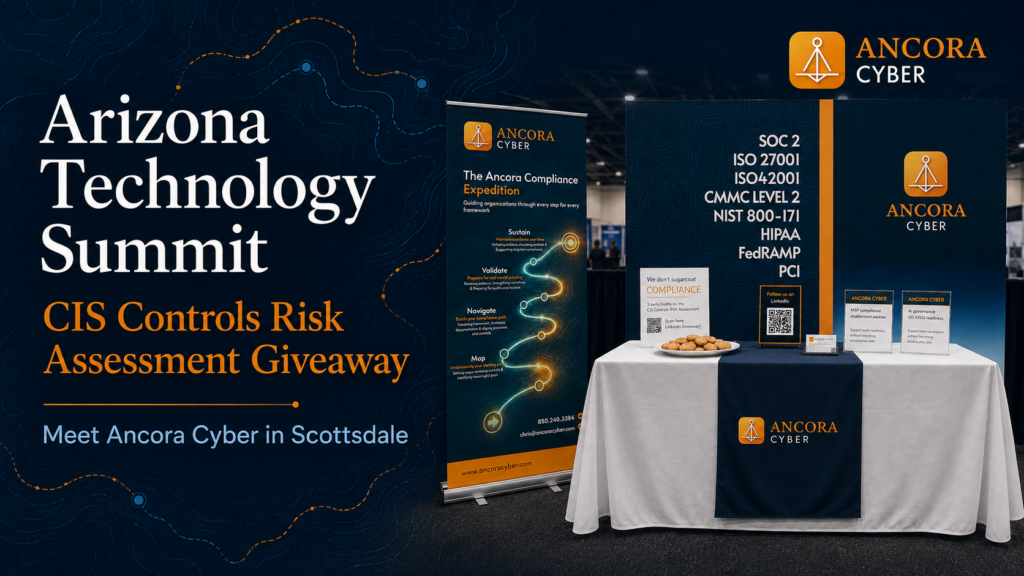
Ancora Cyber will be at the Arizona Technology Summit on Tuesday, August 25, 2026, at the Grand Hyatt Scottsdale Resort in Scottsdale, Arizona.
This will be our first conference as Ancora Cyber. If cybersecurity compliance, customer requirements, or security governance are on your plate, stop by our booth, grab a cookie, and tell us what you are working toward.
We will also be giving one organization a complimentary CIS Controls Risk Assessment.
FERPA Readiness for Education Organizations: Why It’s More Than a Compliance Exercise

FERPA readiness involves more than policies and annual training. Education organizations need visibility into where student information lives, who can access it, which vendors process it, and how governance decisions are documented and maintained.