CMMC Readiness Fails When Documentation and Evidence Lag Behind Implementation
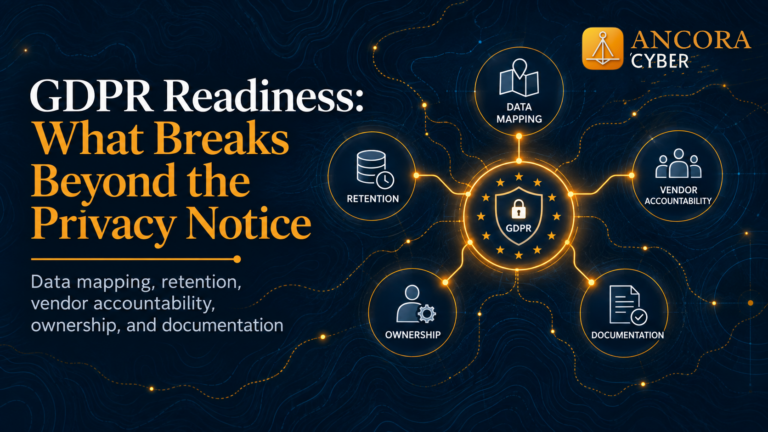
A polished privacy notice can describe a privacy program that does not actually exist.
The real test of GDPR readiness happens behind the notice.
Can your organization identify where personal data enters the business, where it moves, who can access it, which vendors receive it, how long it is retained, and what happens when it should be deleted?
Can the people responsible for those processes explain them?